Case study

VECTOR/SEC — Cybersecurity Assessment Platform

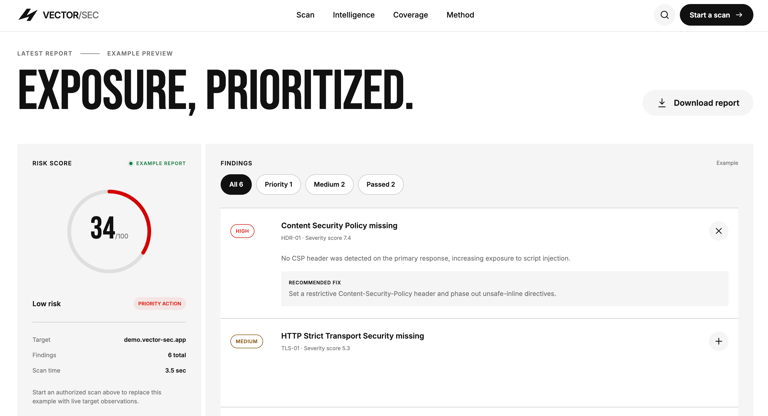
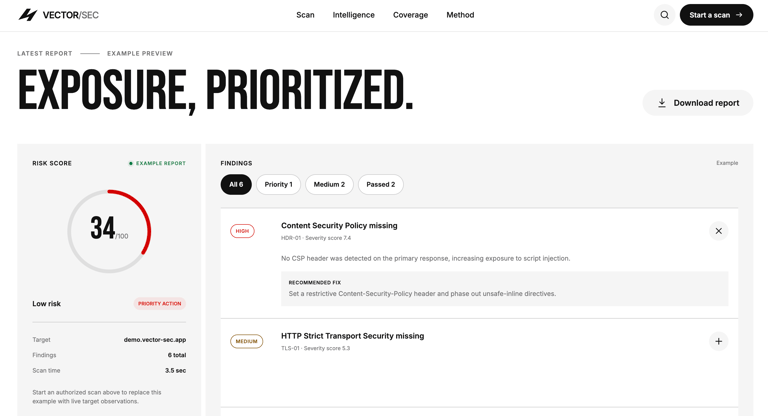
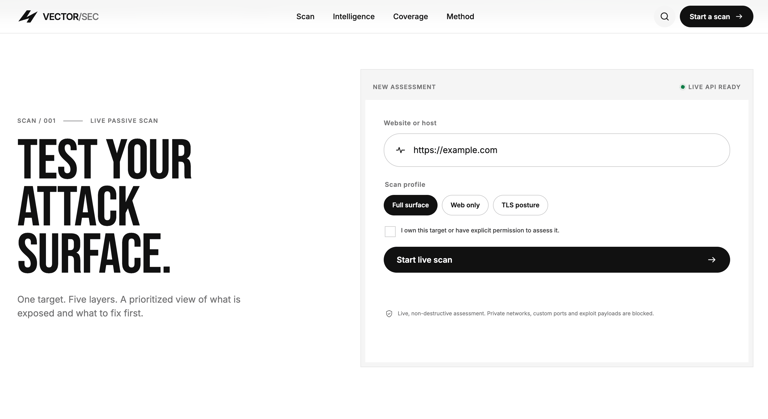
VECTOR/SEC is a security assessment platform designed to help users evaluate the publicly observable security posture of a website through a constrained, passive scanning workflow. It combines a photography-led interface with a Node.js assessment engine, presenting technical checks through a clear dashboard with prioritized findings, risk scoring, and actionable remediation guidance.

Category
Dashboards & systems
Timeline
1 day
Result
Built a guarded passive security assessment MVP with risk scoring, prioritized findings, remediation guidance, automated tests, and downloadable JSON reports.
VECTOR/SEC — Cybersecurity Assessment Platform — screenshot

About the project

Built with React and Vite, the platform allows users to submit a public HTTP or HTTPS target and receive an assessment covering DNS resolution, HTTP status and redirects, security headers, cookie attributes, mixed content, and TLS certificate health. A guarded Vercel serverless endpoint validates targets, rejects private and reserved IP addresses, restricts ports, limits requests, and applies rate limiting to reduce abuse.

The reporting interface includes scan progress, a visual risk score, severity-based finding filters, and downloadable JSON reports. Automated tests cover target normalization, unsafe-target rejection, finding analysis, and risk scoring.

VECTOR/SEC is an MVP for preliminary security triage, not a full vulnerability scanner or a replacement for penetration testing.
Built with

ReactViteJavaScriptNode.jsVercel Serverless FunctionsHTTP/HTTPSDNSTLSWeb SecuritySecurity HeadersRisk ScoringAPI SecurityRate LimitingAutomated TestingResponsive UI

Planning something similar?

Tell us about your idea and we’ll reply within 24–48 hours.

Get in touch